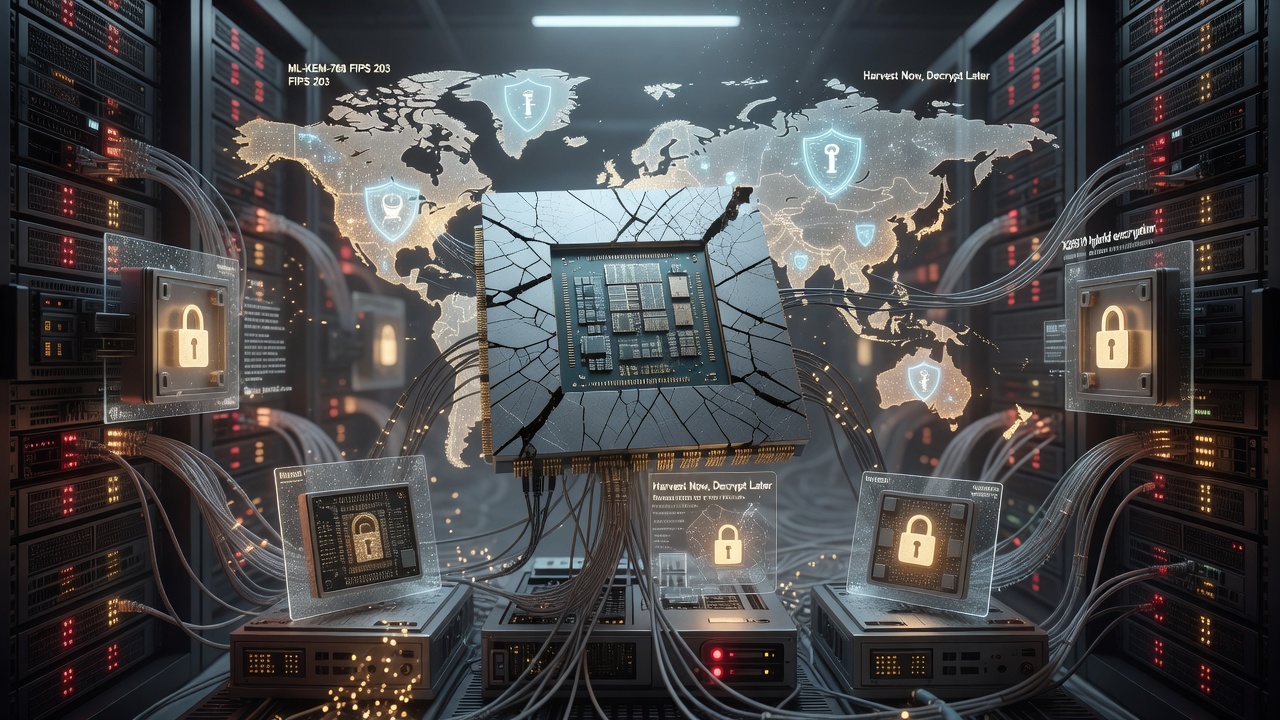
Encrypted data stolen today could be read a decade from now, once quantum computers mature enough to break current public-key cryptography. Cloudflare is moving to close that window with the closed beta launch of its Post-Quantum (PQ) GeoKey Manager, a new component of its Data Localization Suite that binds private decryption keys to specific geographic regions using cryptography already standardized by the U.S. National Institute of Standards and Technology. General availability across Cloudflare's network is planned for the first quarter of 2027.
Why geography and quantum risk are now the same problem
Two pressures have converged on enterprises that rely on global networks: regulators increasingly demand that sensitive data, and the keys that unlock it, stay within national or regional borders; and cryptographers warn that adversaries are already harvesting encrypted traffic today with the expectation of decrypting it once quantum computers become capable enough. This is the so-called "Harvest Now, Decrypt Later" threat. Data with long shelf life - financial records, health data, government communications - is especially exposed, because what looks unbreakable today may not stay that way for the full duration such data needs protection.
Cloudflare's answer ties these two concerns together. The PQ GeoKey Manager does not just encrypt data more strongly; it governs precisely where in the world a private key is allowed to be reconstructed and used, and it does so with cryptographic primitives designed to resist both classical and quantum attacks.
How the architecture keeps keys geographically fenced
The system rests on a hybrid key encapsulation approach that pairs ML-KEM-768, a lattice-based algorithm standardized by NIST as FIPS 203, with the classical elliptic-curve method X25519, following the Hybrid Public Key Encryption framework defined in RFC 9180. Because both algorithms must be broken for confidentiality to fail, the design protects against future quantum breakthroughs without abandoning the proven security of current elliptic-curve cryptography. Symmetric operations rely on AES-256-GCM authenticated encryption and HKDF-SHA-256 key derivation, both well-established standards.
- Encrypted customer data and the public keys used to wrap it travel globally through Cloudflare's Quicksilver key-value store, reaching edge servers anywhere on the network.
- The symmetric regional root keys needed to actually unwrap and use those private keys never travel through that global system. They remain confined to a control-plane service backed by on-premises HashiCorp Vault clusters.
- Before an edge server can receive a regional root key, it must prove its physical identity and location through a hardware Trusted Platform Module, verified against Cloudflare's Zinc server inventory system.
- Once authorized, keys live only in volatile Linux kernel keyrings - never written to disk - so a reboot or power cycle erases them automatically.
- If a server outside the authorized region ever receives a request needing a root key it was never issued, the system fails closed, dropping the request rather than risking cross-border decryption.
This separation of globally distributed ciphertext from regionally confined root keys is the structural core of the system. Even if encrypted material is replicated worldwide for performance reasons, the ability to decrypt it stays locked to approved hardware in approved locations.
From attribute-based encryption to a quantum-ready model
Cloudflare's geographic key controls are not new. The company introduced geographic key isolation in 2017 and refined it in 2022 using Ciphertext-Policy Attribute-Based Encryption, a scheme well suited to flexible, multi-region access rules. The redesign was necessary because no standardized, production-ready post-quantum version of attribute-based encryption currently exists. Rather than wait, Cloudflare rebuilt the system around HPKE, a more mature and already-standardized framework capable of supporting hybrid classical-quantum encryption today.
That choice reflects a broader pattern across the security industry: where fully post-quantum solutions remain immature for a given cryptographic function, hybrid constructions are becoming the practical bridge, preserving current protections while adding forward-looking resistance to quantum attacks.
What this means for enterprises and regulators
The closed beta is initially limited to enterprise customers using Cloudflare One Zero Trust services, including Magic WAN, Tunnel, and Gateway, with full integration into Cloudflare's content delivery network planned ahead of the 2027 general release. For organizations bound by regulations such as the GDPR or financial-sector data residency rules, the appeal is straightforward: demonstrable, hardware-attested proof that private keys never leave an approved jurisdiction, combined with protection against decryption threats that may not fully materialize for years. Whether this approach becomes an industry baseline will depend on how other major infrastructure providers respond, but it signals that data sovereignty and post-quantum readiness are no longer being treated as separate engineering problems.