The way companies defend their networks is undergoing a structural shift, and the numbers reflect it. According to MarketsandMarkets™, the global Zero Trust Network Access market will grow from USD 1.34 billion in 2025 to USD 4.18 billion by 2030, a compound annual growth rate of 25.5 percent. The forecast, released July 8, 2026, points to a cybersecurity model that has moved from niche concept to default expectation across industries managing cloud infrastructure and remote workforces.
Why the old perimeter stopped working
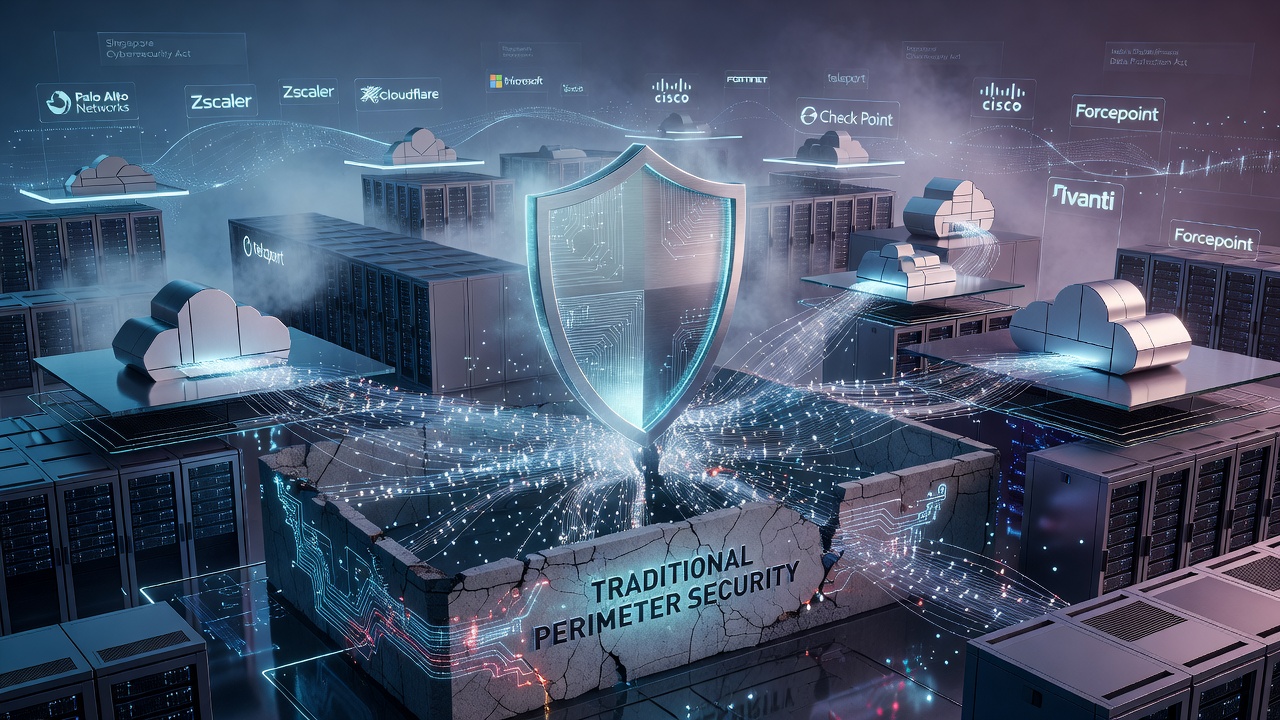
For decades, corporate security operated on a simple premise: build a strong wall around the network, and anything inside the wall could be trusted. That model made sense when employees worked from fixed offices and applications lived on internal servers. It makes far less sense now. Cloud platforms, remote staff, contractors, and personal devices have dissolved the boundary that perimeter security relied on. Once an intruder breached the outer wall, they often moved freely inside.
Zero Trust Network Access rejects that assumption entirely. Instead of granting broad access once a user is inside the network, it verifies every single connection request, continuously, based on identity, device condition, and context. Access is granted only to the specific application needed, for as long as needed, rather than to the network as a whole. This "never trust, always verify" principle limits what an attacker can reach even after a successful breach.
Cloud, hybrid work, and the push toward SASE
The expansion of hybrid and multi-cloud environments is the clearest driver behind this growth. Organizations running workloads across multiple cloud providers need a way to enforce consistent access rules regardless of where data or applications sit. ZTNA is increasingly bundled into Secure Access Service Edge, or SASE, platforms, which combine networking and security functions into a single cloud-delivered service. That integration gives security teams broader visibility over traffic and users while narrowing the attack surface available to intruders.
Artificial intelligence is reinforcing this shift. Behavioral analytics tools now flag unusual login patterns or device anomalies in real time, allowing access policies to adjust automatically rather than relying on static rules. This matters particularly for third-party users, contractors, and employees using personal devices, groups that have historically represented a weak point in enterprise defenses.
Where growth is concentrated
Large enterprises remain the dominant adopters, given the complexity of their hybrid environments and the volume of external parties they must grant access to. The solutions segment, covering agent-based, agentless, and universal ZTNA deployments, is expected to account for the largest share of market revenue through the forecast period.
Asia Pacific is projected to post the fastest regional growth. Digital transformation efforts in China, India, Japan, and Australia, spanning fintech, smart city projects, and critical infrastructure, are increasing the urgency around identity-based access control. Regulatory developments are reinforcing this trend, including Singapore's Cybersecurity Act, India's Digital Personal Data Protection Act, and Australia's critical infrastructure security reforms, all of which push organizations toward stronger verification and data protection standards.
A competitive field, a long runway
Vendors including Palo Alto Networks, Zscaler, Cloudflare, Microsoft, Check Point, Teleport, Cisco, Fortinet, Ivanti, and Forcepoint are competing to extend their platforms through deeper SASE integration and adaptive policy engines. The direction of travel is consistent across the industry: access control built around identity and context, not network location.
The implications extend beyond corporate IT budgets. As regulators tighten requirements around data protection and continuous verification, Zero Trust principles are becoming less a competitive advantage and more a baseline expectation, reshaping how organizations think about trust itself in an era where the network edge no longer has a fixed location.